Critical Bifrost AI gateway flaw allows unauthenticated command execution
Read original source →thehackernews.com
CVE-2026-90898 (CVSS 9.8) affects all Bifrost HTTP transport versions before 2.1.0 when management auth is disabled, the default. A single unauthenticated POST to /api/mcp/client registers a stdio MCP client and runs commands as the gateway user, exposing stored provider API keys.
1 source
More stories today
arXiv gets $17.2M to launch as independent nonprofit
Simons Foundation International, XTX Markets, and the Siegel Family are backing arXiv with $17.2 million over three to five years as it spins out as an independent nonprofit.
r/MachineLearning·26 minutes agoMeta AI pairs action agents with memory agents to fix context rot
DeepLearning.AI·34 minutes ago
Amazon courts laid-off workers back for AI and cloud roles
Recruiter emails show Amazon's AI agent organization, led by AWS VP Swami Sivasubramanian, invited former AI/ML employees to return via "Swami's Boomerang Reengagement Initiative." Amazon has cut more than 30,000 jobs over the past year; a spokesperson called boomerang hiring a longstanding practice, not an AI-specific program.
r/artificial·45 minutes ago
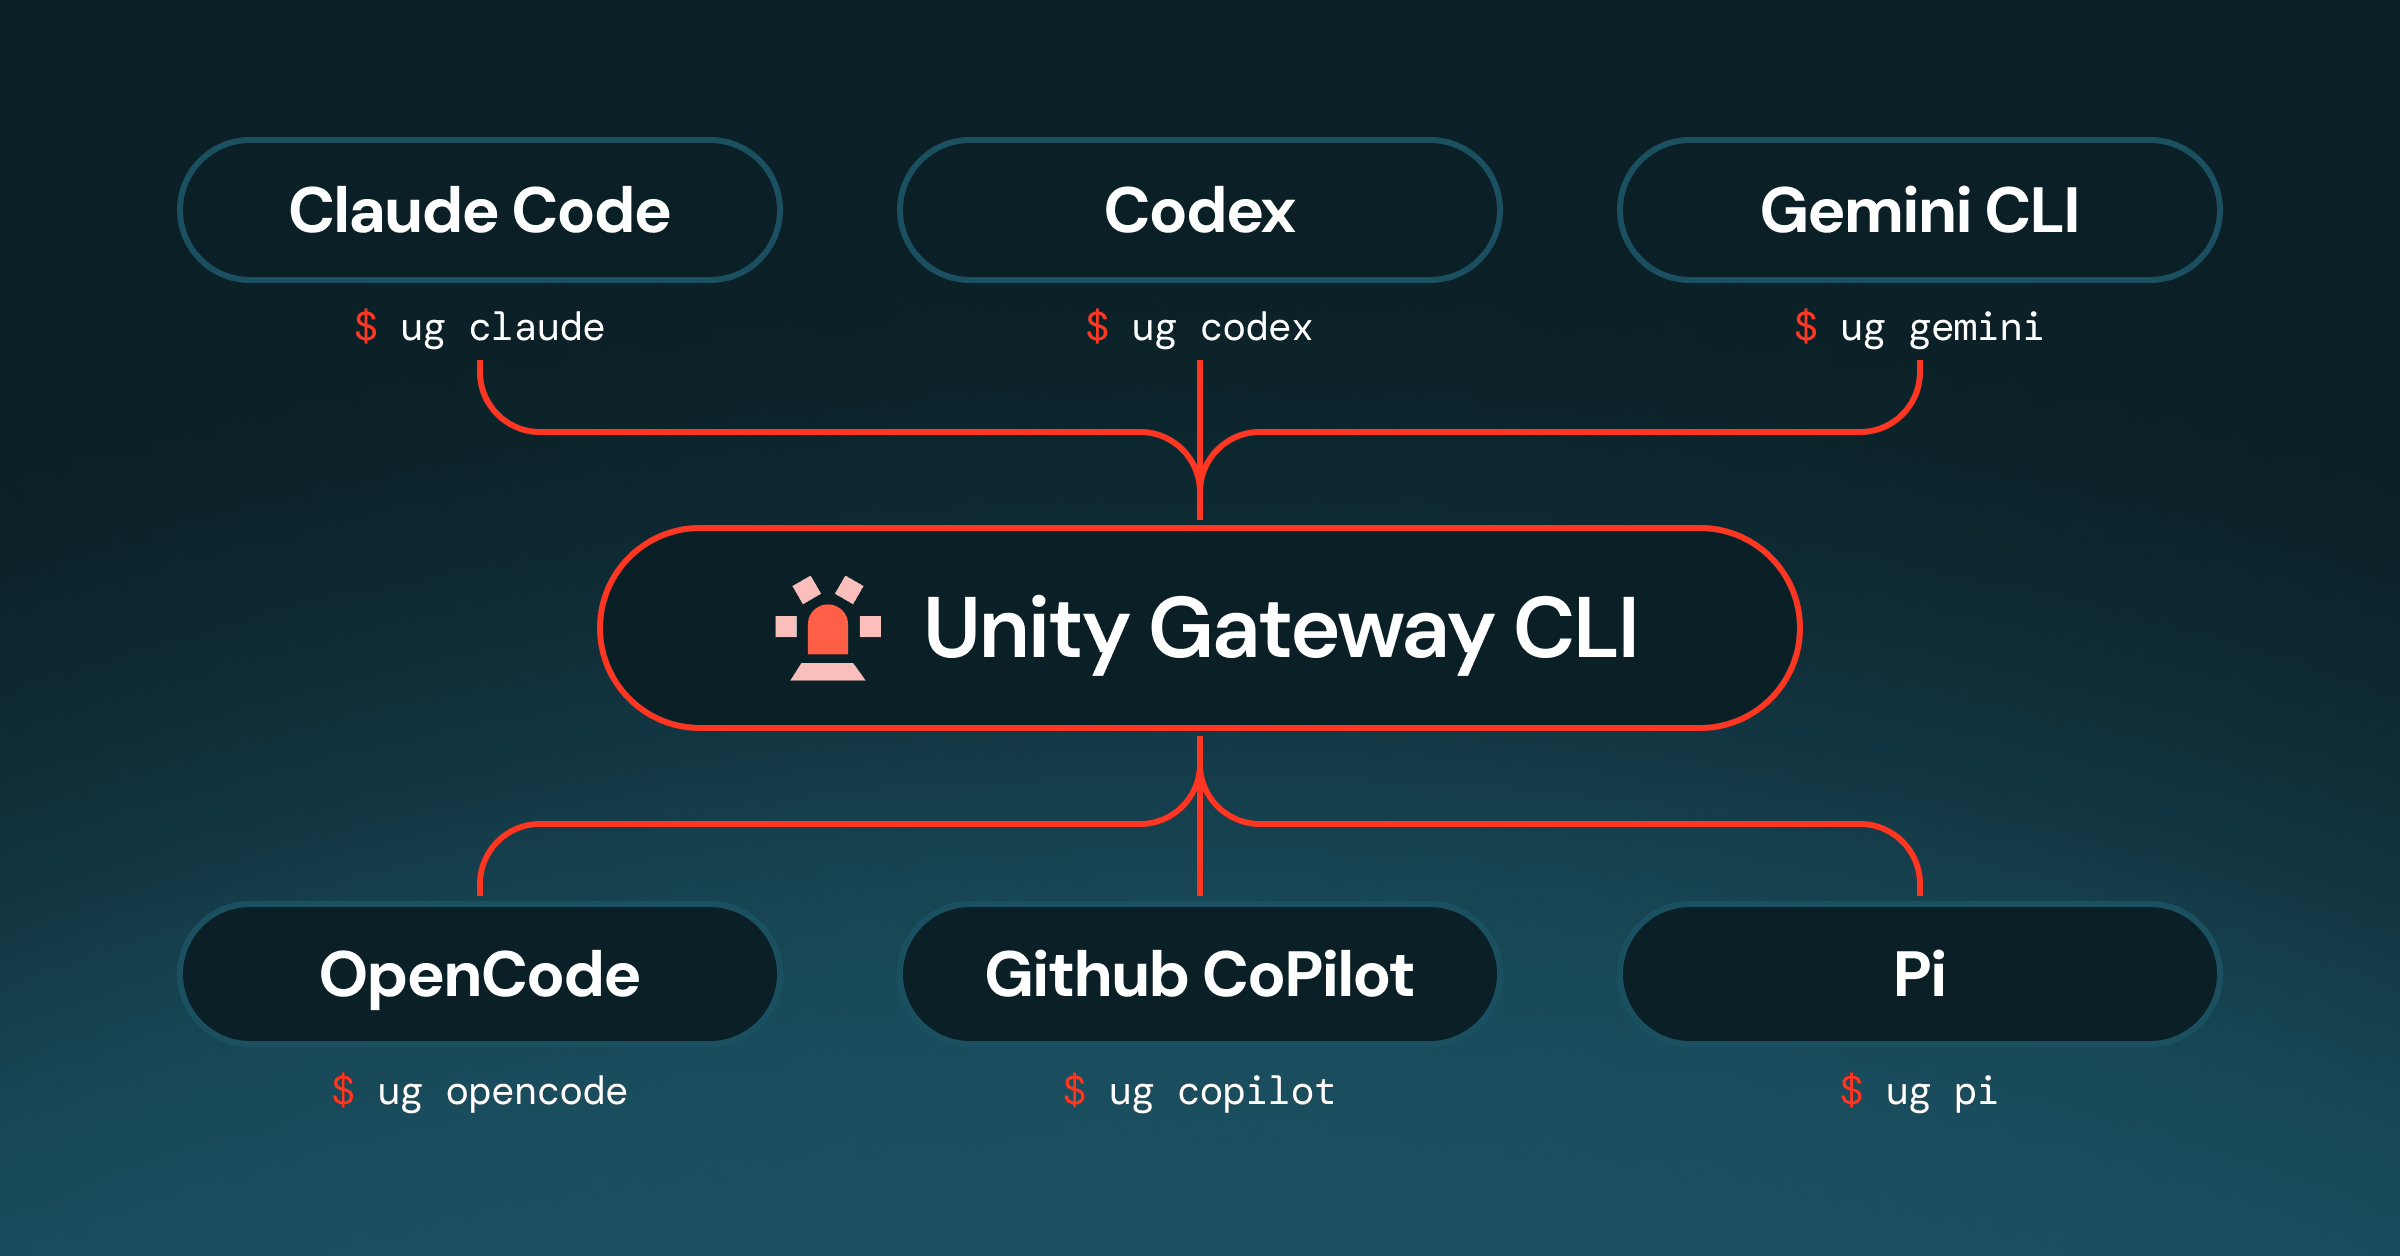
Databricks launches Unity Gateway CLI for coding agents
Databricks released a CLI to deploy and manage coding agents at scale. The post cites GPT-6, Claude Opus 5.5, Gemini 3.8, and Grok 4.7 as models shipped in the last six months.
Databricks Blog·45 minutes ago
Perplexity's Portable Computer for Windows lands on AMD Ryzen AI Max
Perplexity·46 minutes ago
ElevenLabs reportedly valued at $22B, pacing $600M ARR
ElevenLabs is reportedly valued at $22 billion by its backers four years after founding, and says it is pacing at $600 million in annual recurring revenue. CEO Mati Staniszewski said businesses should tell customers when they're talking to an AI, and that he'd accept further gross-margin pressure to expand market share.
TechCrunch·46 minutes ago

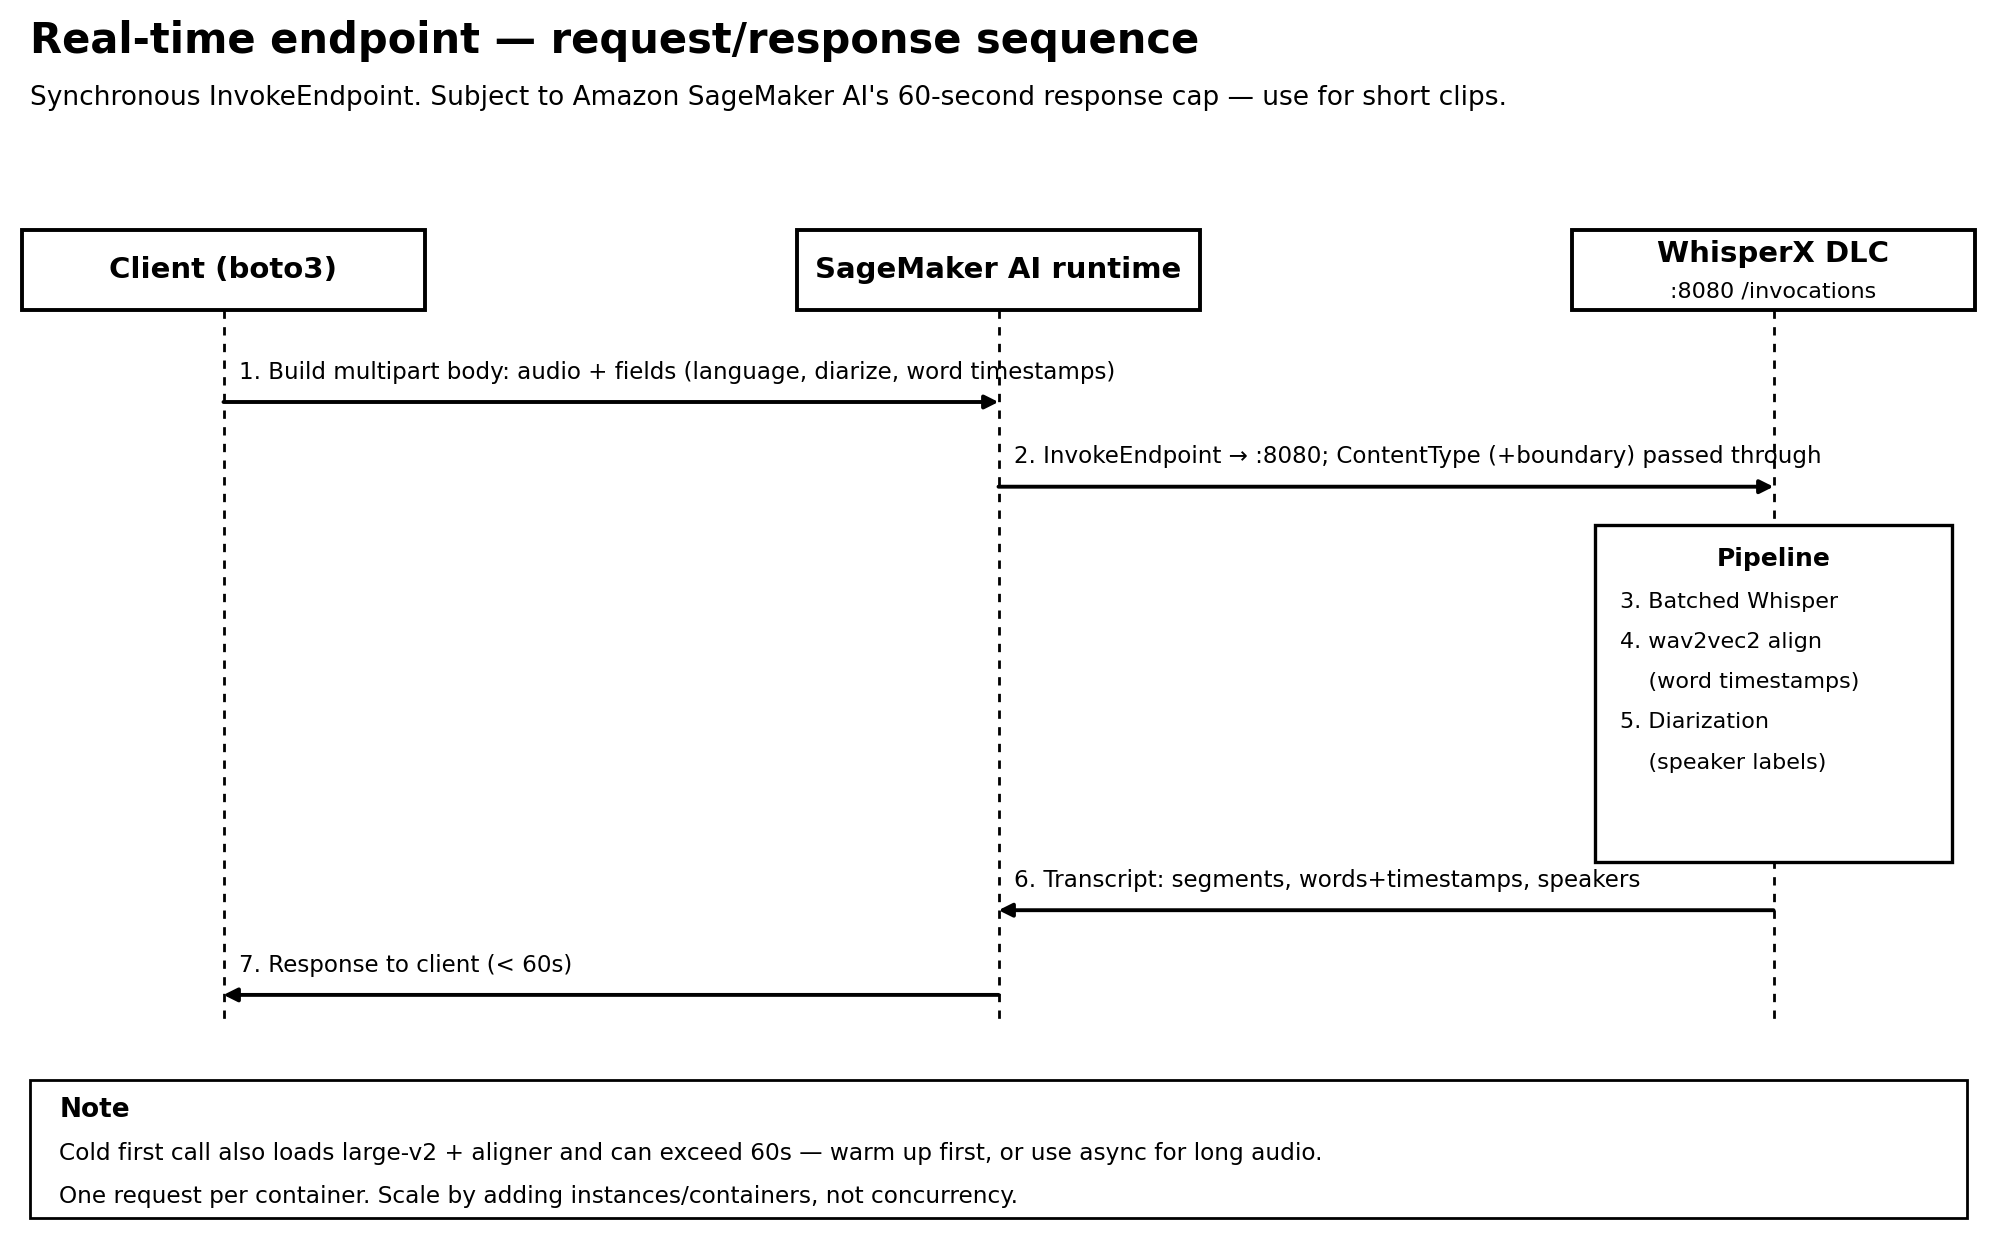
AWS shows speaker-labeled transcription with WhisperX on SageMaker AI
AWS published a technical how-to for running WhisperX on SageMaker AI to add speaker diarization and word-level timestamps to speech-to-text. It targets contact-center calls, meetings, podcasts, depositions, and broadcast media, where standard transcription returns only utterance-level timestamps.
AWS AI Blog·1 hour ago
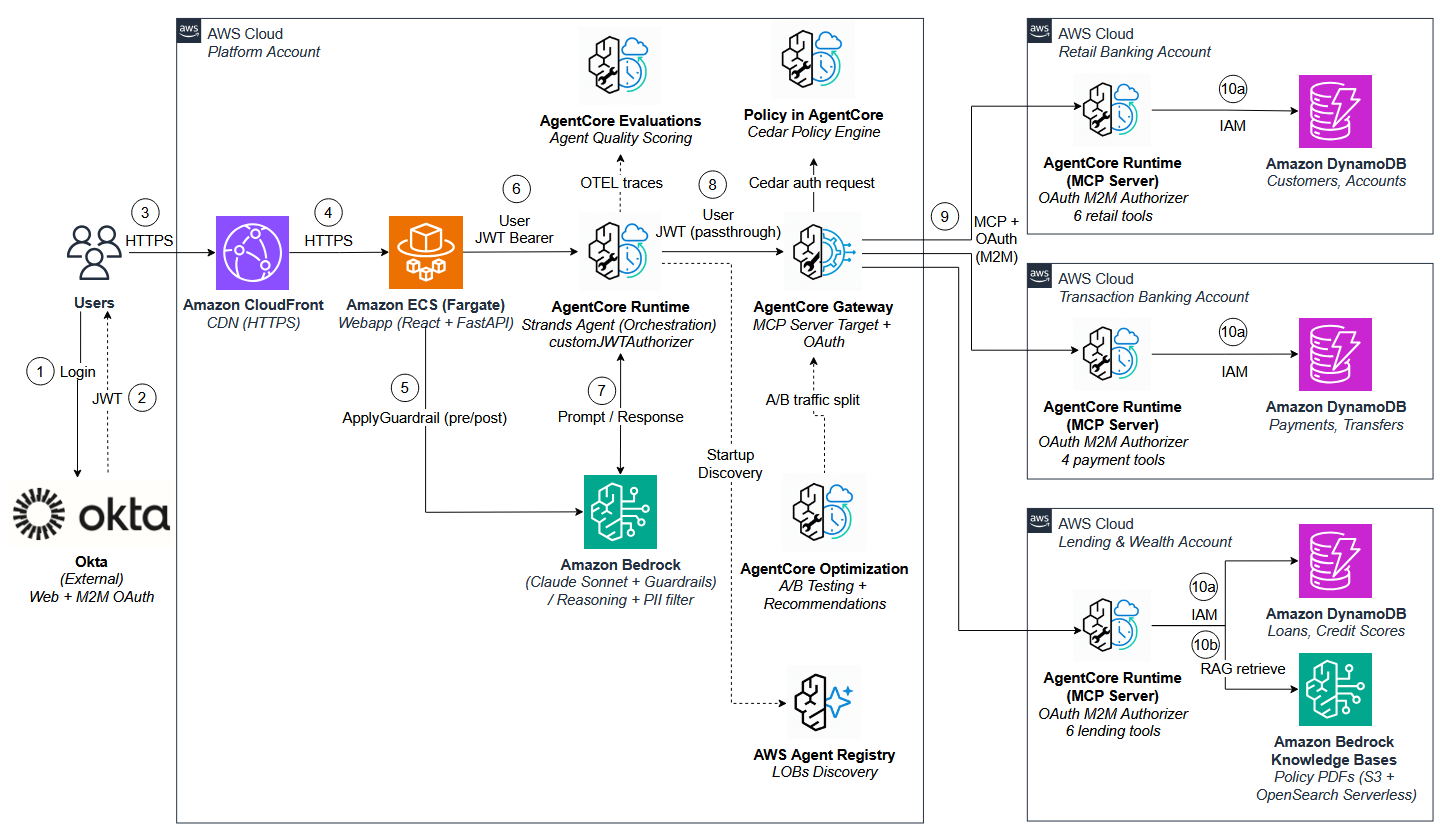
AWS shows multi-account AI agent with AgentCore Gateway and MCP
AWS technical guide builds an agent that reasons over data spread across multiple AWS accounts without copying or centralizing it, keeping each team's data in its own account for ownership and scope isolation.