Unpatched LMCache flaw lets attackers run code on LLM cache servers
Read original source →thehackernews.com
JFrog disclosed CVE-2026-105192 on October 7 with a 9.8/10 severity score; no fixed version exists. The flaw affects LMCache 0.3.9 through 0.5.5, plus 0.5.6 release candidates and the dev branch.
1 source
More stories today
deepagents adds dynamic tool loading for skills
Harrison Chase·20 minutes agoOpenAI's Decisions API hits public beta, powered by GPT-6 Luna
The Decisions API returns structured probabilities, choices, and scores instead of generated text, and OpenAI says it makes decisions up to 10x faster than GPT-6 Luna via the Responses API. Input is billed at 10 cents per million tokens with no output charge.
Vercel Blog·22 minutes ago
NVIDIA and Microsoft bring AI agents to Windows with RTX Spark
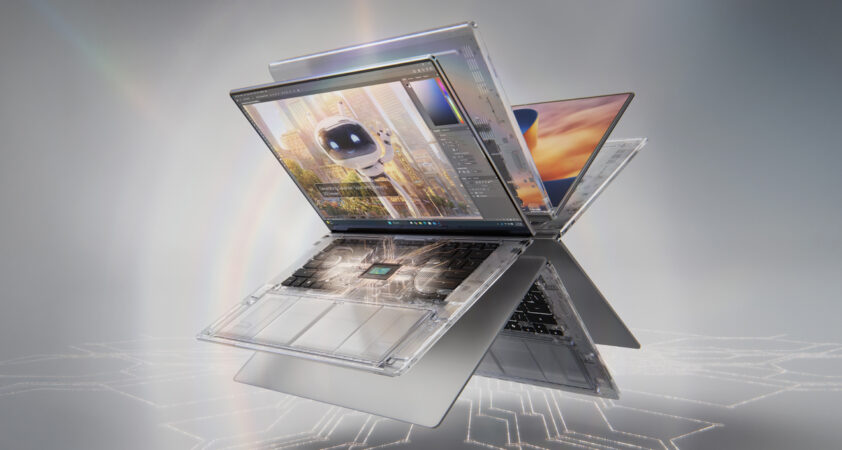
At a San Francisco event, Jensen Huang and Satya Nadella outlined co-engineered hardware and software for agents on Windows PCs. Microsoft announced general availability of Microsoft Execution Containers (MXC), OS-level infrastructure for running agents safely in the background.
blogs.nvidia.com·33 minutes ago
Engineers let GPT-6 Astra drive a Toyota Corolla to In-N-Out
Three Axiom engineers wired GPT-6 Astra to windscreen cameras and a 2024 Corolla's power steering, and it navigated the drive-thru with no prior coaching. GPT, Claude, and Grok were tested; only one succeeded.
Wired·33 minutes ago

Genie Ontology infers business context for data queries
Databricks·35 minutes ago
AWS details access control for RAG with Amazon Quick and Bedrock
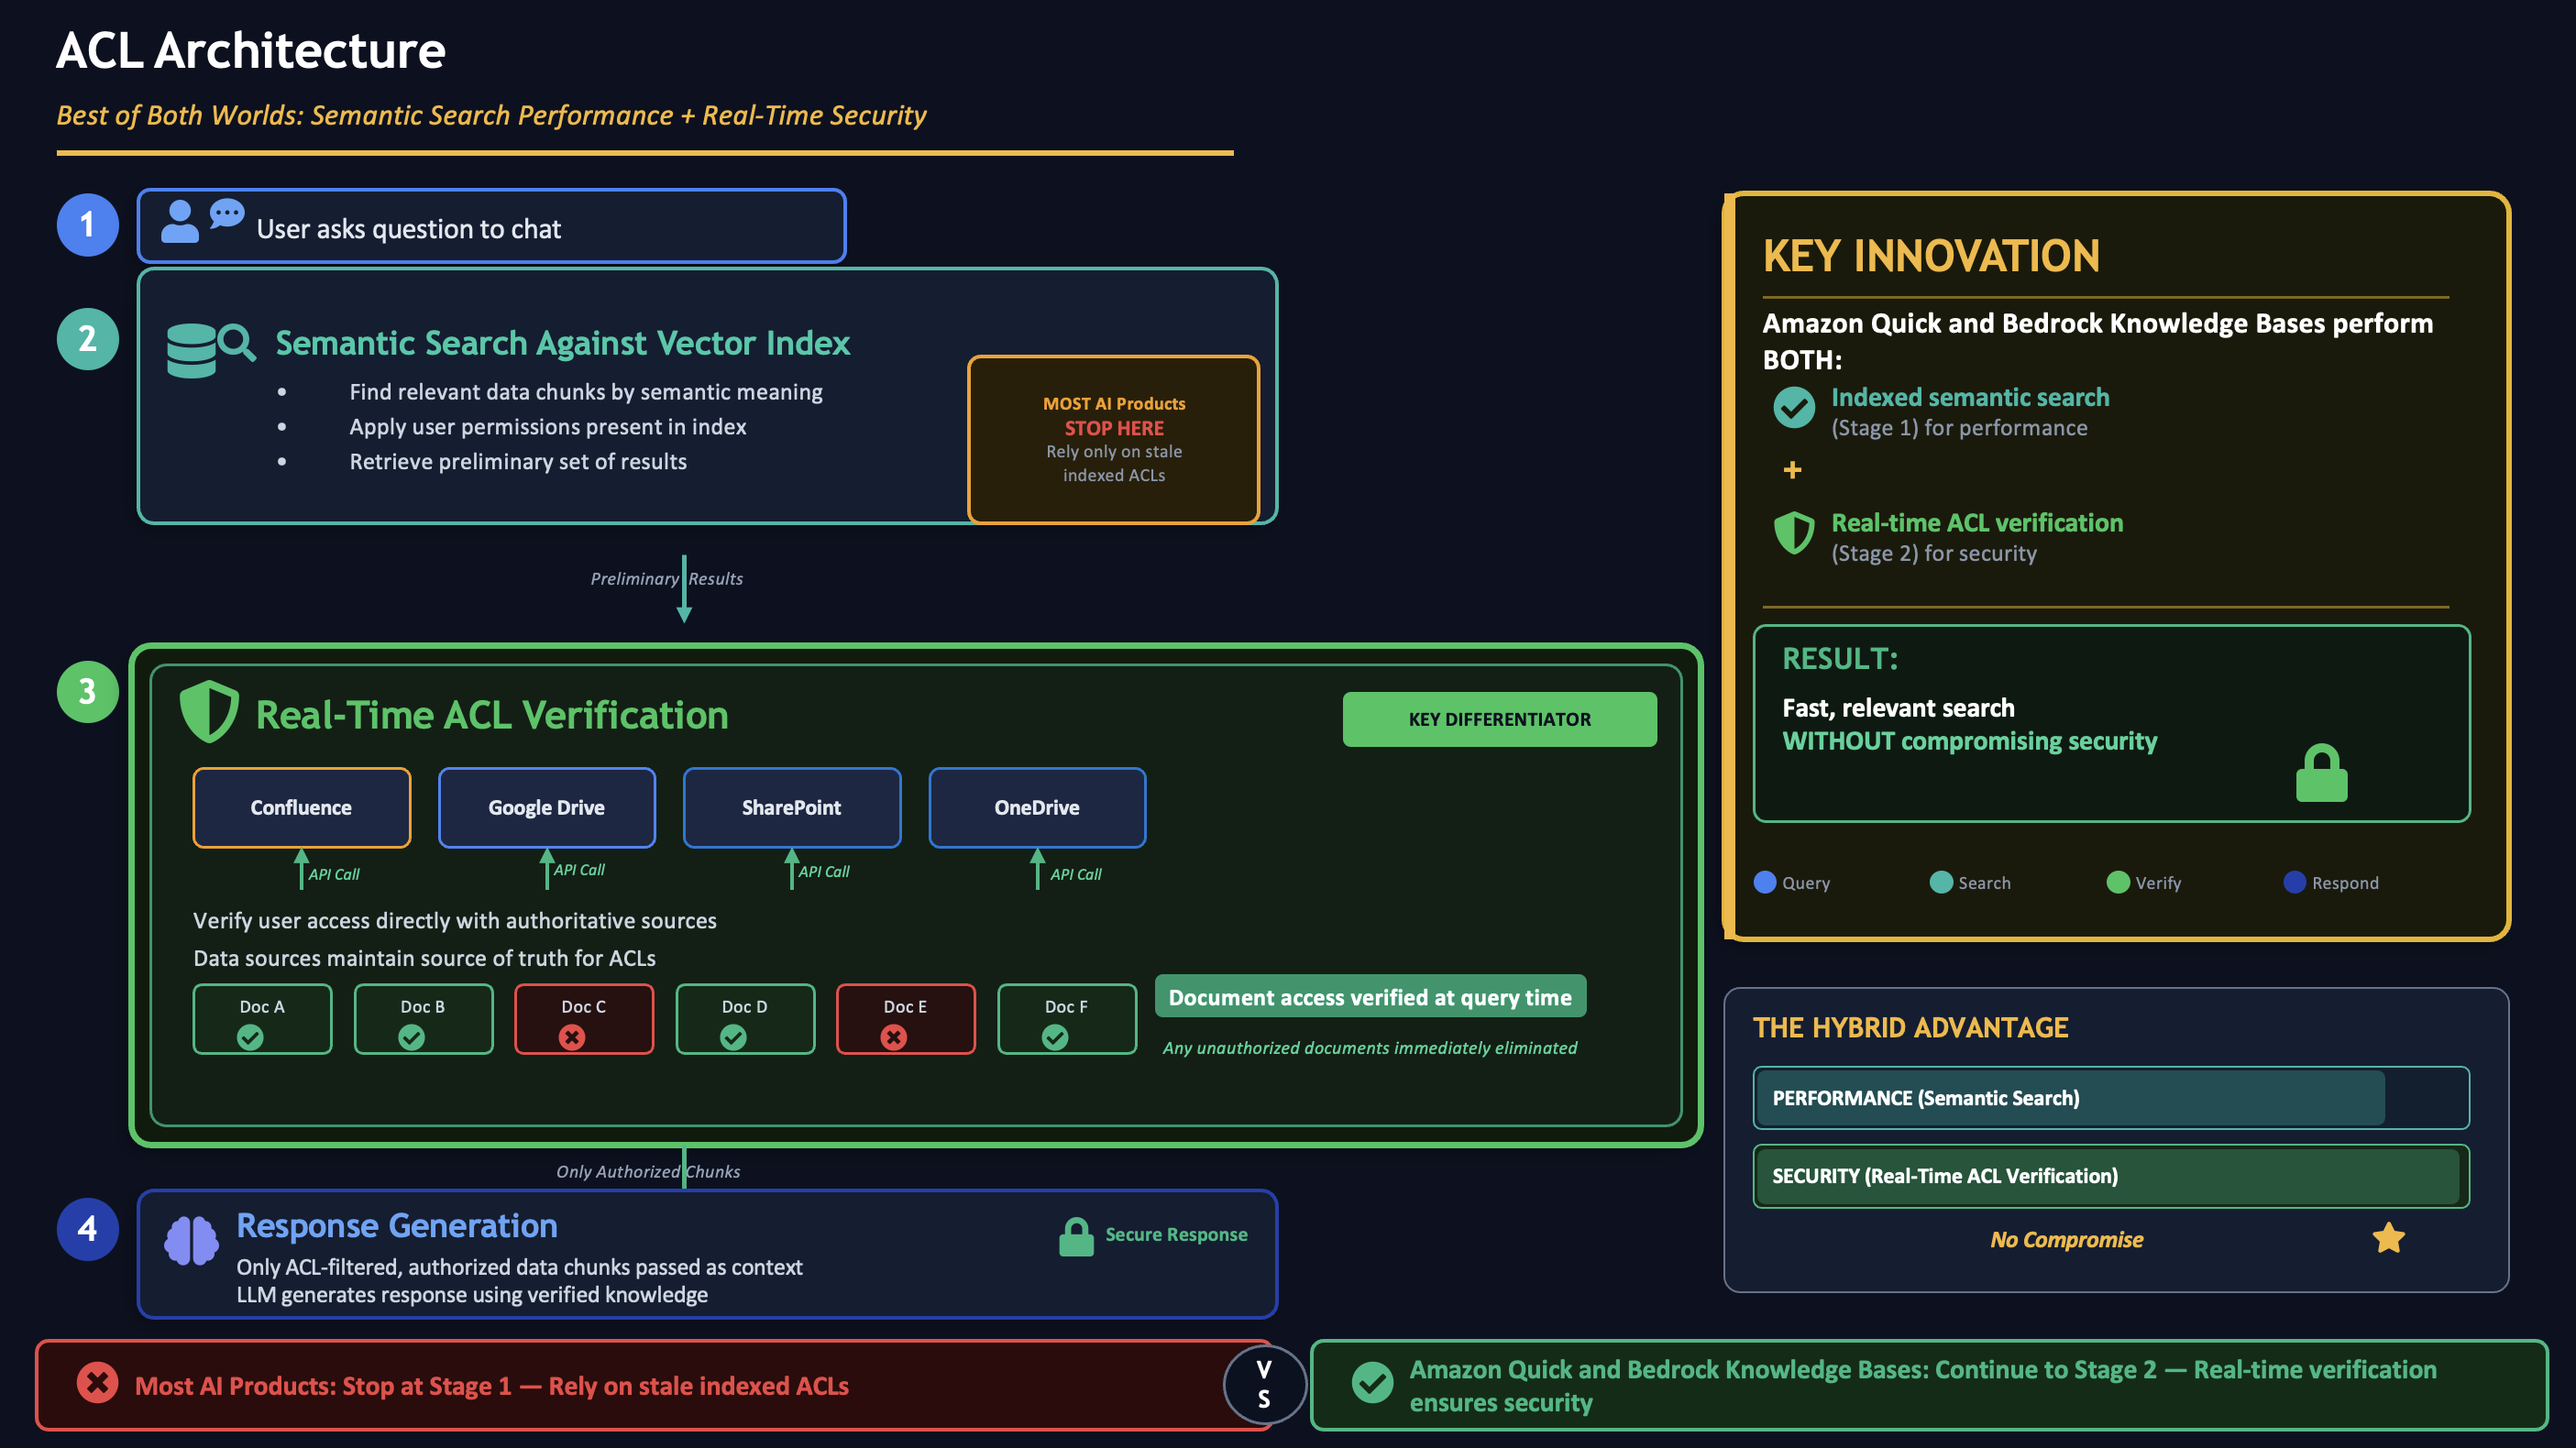
AWS outlines how to enforce permission structures when RAG pulls from SharePoint, Google Drive, and Confluence, sources that carry sensitive data governed by complex permissions.
AWS AI Blog·44 minutes ago
Meta's Muse AI agent arrives on iPad a month after iPhone debut
Muse has topped 6.6 million installs since launching on iOS and Android on September 8, per Sensor Tower estimates. The iPad release adds connectors including Asana, Canva, Figma, GitHub, QuickBooks, Notion, and Zoom, plus retail partners Best Buy, Gap, Sephora, Walmart, and Wayfair.
TechCrunch·47 minutes ago

NVIDIA taught robots to assemble GB300 tester trays
NVIDIA's Seattle Robotics Lab automated two GB300 tray tasks: busbar assembly (grasp, insert, screw at 16 locations) and multi-connector insertion of two large and two small connectors into tight-clearance sockets. The lab calls it one of the hardest problems in its nine years, testing where end-to-end learning beats a modular stack.
NVIDIA Developer Blog·57 minutes ago
