OpenCode flaw lets malicious MCP servers run code on Windows, WSL
Read original source →thehackernews.com
Pillar Security rates it critical at 9.8/10: a hijacked MCP server's OAuth authorization endpoint was passed unescaped into a PowerShell command during sign-in. Anomaly fixed it in 1.18.33 on September 28 without a CVE or advisory, leaving 1.0.137–1.18.32 unflagged by scanners.
1 source
More stories today
Hackers turn exposed AI models into cybercrime tools
Researchers uncovered a technique to subvert safety guardrails on exposed AI models, repurposing them for cybercrime, per Bloomberg's newsletter. Details sit behind a paywall.
Bloomberg Technology·1 hour ago
Apollo's Slok: AI data center buildout is a critical US growth driver
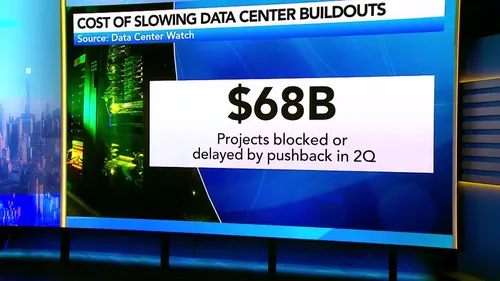
Apollo chief economist Torsten Slok calls the AI buildout "a very, very critical driver of growth at the moment" for the US economy, flagging risks from delays in data center construction. He also discusses the prospect of an AI-induced bank run.
Moises partners with SoundCloud on stem separation integration
SoundCloud artists can export tracks into Moises for mixing, mastering and stem separation; each company's artist subscribers get two-month trials of the other's paid tier. Both frame the deal around an 'artist-first' responsible AI ethos.
Music Ally·1 hour ago

Reddit user: Qwen Flash Next at IQ2 beats Q8 of 27B model
A LocalLLaMA user reports that a heavily quantized Qwen Flash Next at IQ2 outperforms a Q8 27B model on complex prompts, contradicting community advice that Q8 would win outright.
r/LocalLLaMA·1 hour agoTK Elevator uses agentic AI to brief technicians before jobs
TK Elevator built agents on Azure AI Foundry and Azure Databricks that brief service technicians before they reach an elevator, then capture what they learn via a voice debriefing agent. Insights from its Digital Operations Centers feed the agents.
YouTube·1 hour ago
Solo dev builds cyberpunk pixel-art game with Claude Code
A developer has spent about a month on City of Animals, a 2D cyberpunk pixel-art side-scroller mixing Monkey Island-style adventure with Huntdown- and Replaced-inspired combat. They say Claude Code let them pursue both directions solo instead of picking one.
r/ClaudeAI·2 hours ago
Rumor: next Chinese AI models to release within 7 days
Kimmonismus·2 hours agoAnthropic interpretability researcher on models that think badly
Emmanuel Ameisen, an interpretability researcher at Anthropic, describes a model that knew the answer was 12 but kept outputting 36, then wrote in all caps that it was possessed by a demon. He explains why a model thinking badly is so hard to catch.
YouTube·2 hours ago