Langflow RCE flaw CVE-2026-105740 targeted in 1,423 honeypot attempts
Read original source →thehackernews.com
The authenticated RCE (CVSS 9.9) affects Langflow versions before 1.9.0; any logged-in user, including non-admins, can run OS commands by adding an MCP server with stdio transport. The command field passes unvalidated to bash -c, and the env field allows LD_PRELOAD or PATH injection.
1 source
More stories today
EasyComfee V2 launches as open-source creative studio on ComfyUI
Built by a Reddit user who found ComfyUI node-wiring slow and models too large for their GPU, EasyComfee bundles Image, Video, VFX, Lip Sync, Music, Voice and Genjutsu modes into one studio.
r/ComfyUI·1 hour ago
OpenAI trains activation classifiers to monitor model safety
Since GPT-5.6, OpenAI has run activation classifiers on all assistant completions, reading a model's internal activations to flag misaligned behavior. OpenAI says probes block policy-violating turns mid-stream and resist jailbreaks better than much larger text classifiers.
OpenAI Alignment·1 hour ago
Apple's J595 home robot may launch by 2027 for $1,000+
Apple is developing an AI-driven roaming home robot, code-named J595 and possibly named HomeView Ultra, targeting a $1,000+ price by 2027, with delays possibly pushing it to 2028. Prototypes date to 2018; features reportedly include FaceTime calls and automatic lighting.
Ars Technica·1 hour ago
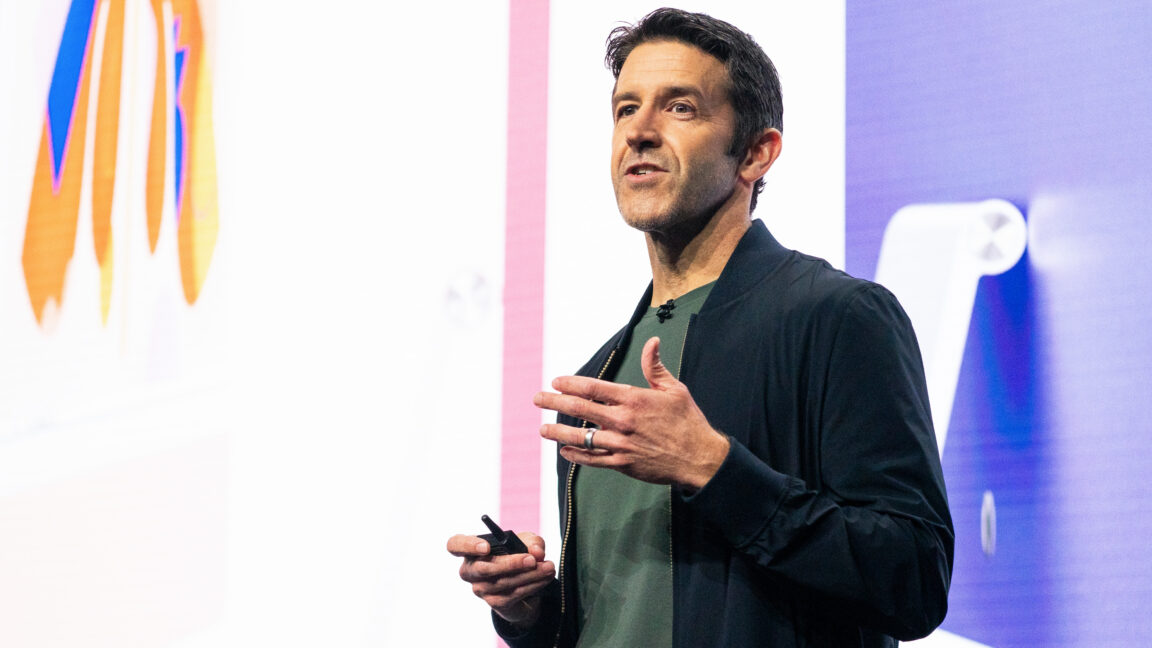
Sam Altman discusses AI's future and energy at ADIPEC in Abu Dhabi
OpenAI CEO Sam Altman spoke at the ADIPEC opening ceremony in Abu Dhabi, covering AI's future, energy innovation and human control of the technology. He highlighted the UAE's growing role in AI adoption.
DWS News·2 hours ago
OpenAI introduces LifeVal benchmark for everyday tasks
LifeVal measures how well AI helps people complete daily tasks like finding childcare, managing finances, and handling government paperwork. OpenAI says the benchmark was shaped by feedback from thousands of ChatGPT users on where they most want assistant help.
OpenAI Blog·2 hours ago
Anthropic adds Claude Code rule blocking recreation of existing games
A rule named "tengu_heron_brook" in Claude Code 2.1.314 (released Oct 30) tells Claude to build original or genre games but not recreate a specific existing game, even if renamed. Anthropic engineer Addy Osmani confirmed two sentences were added to Opus 5.5's prompt because using Claude to infringe IP violates usage policy.

NVIDIA AICR preps Kubernetes for Vera Rubin NVL72 on Day One
NVIDIA's AI Cluster Runtime, part of the DSX AI Factory Platform, captures tuned configs as reusable recipes and validates running clusters so Kubernetes is ready for Vera Rubin NVL72 compute trays at launch. Vera Rubin requires a new GPU driver branch, validated with host-installed R615.23, with early support targeted for R610.
NVIDIA Developer Blog·2 hours ago

BU opens faculty searches in human-centered AI, AI for science
Naomi Saphra·2 hours ago