RatHat Android trojan uses generative AI to control infected devices
Read original source →securityweek.com
Zimperium found RatHat, an Android trojan distributed via smishing and malvertising that uses generative AI to navigate device interfaces in real time and monitors input at the hardware level to reconstruct PINs, passwords, and patterns. It abuses Accessibility Services and autonomous local ADB self-pairing to escape the app sandbox and run shell-level daemons.
How this story unfolded
10 days · 3 reports · from Sep 18
More stories today
OpenAI previews Private Safety Processing for API data
Private Safety Processing lets OpenAI review related API requests for safety without retaining prompts or responses, with records staying in the customer's environment. An automated safety agent reviews them, and OpenAI personnel cannot access the content.
OpenAI Developers·22 minutes ago
SecurityDataPipeline.com launches as educational resource for AI-era security data
The ungated site explains how security data pipelines cut SIEM ingestion costs while preserving detection coverage. It also covers preparing the data layer for AI-driven security operations.
Dark Reading·28 minutes ago

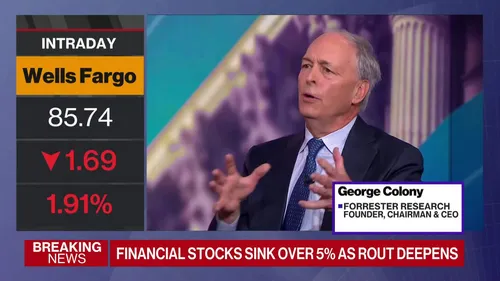
Forrester's Colony: AI investment to continue despite tech selloff
Forrester Research founder and CEO George Colony says the AI boom may be entering a new phase, with custom chips challenging Nvidia's dominance and value shifting toward software. He warns the transition won't be smooth and companies must adapt to AI computing or risk being left behind.
Bloomberg Technology·33 minutes ago
Bloomberg video weighs AI bets against rising capital costs
David N. Miller discusses how higher cost of capital affects AI investment, pointing to flexible financing for hard-to-refinance assets and infrastructure beyond the AI boom. He also covers AI's long-term potential, concentration risks, and why selectivity matters for investors.
Jensen Huang says he mostly uses Perplexity for AI
Filmed in London on October 14, 2026, Huang said "I don't build my own AI. Mostly I use a service called Perplexity." The clip was captured by Kim Isenberg during his Europe tour.
Superintelligence·40 minutes ago
Suleyman: at 10% extinction risk, "we absolutely have to stop"
Microsoft AI CEO Mustafa Suleyman said that if the chance of runaway machine intelligence causing human extinction is really 10%, "we don't just slow down or pause. We absolutely have to stop." The clip comes from ControlAI, which frames such risk estimates as common among AI insiders and scientists.
ControlAI·40 minutes ago
VFlash vision model parses visual world in parallel for Physical AI
Jim Fan·44 minutes ago
Qwen Code v0.26.8 fixes CI linter downloads and RHEL 10 rpm pin
Patch release v0.26.8 keeps ACP parity runtime state out of the workspace and repins the RHEL 10 rpm root to the current stream10 digest. CI linter archive downloads now resume instead of restarting.
Qwen Code Releases·52 minutes ago